Healthcare Pharma & Life Sciences Other Industries
All Services Performance Marketing ChatGPT Ads India · NEW Social Media Marketing SEO & AEO / LLM YouTube Marketing LLM Optimization Brand & Growth Consulting AI Solutions Industries We Serve
Enterprise Hub · All Solutions + Services Growth Transformation AI Transformation Revenue Operations Fractional CGO Growth Operating System Executive Growth Advisory
Clinic Launch Programme (Hub) NABH Consulting India Healthcare Brand Launch Clinic SOP Creation Logo Design (Healthcare) Brand Book Creation Clinic Launch Marketing D2C Brand Launch Clinic Interior Design
Workforce Hub For Employers — post a requirement For Professionals — register Public Openings Training Academy AI Training Flagship
Hawk · CRM Intelligence (NEW) YODA · YouTube Intelligence Angryturtle · GBP Intelligence (NEW) Prism Pulse · Instagram Analytics (NEW) Beacon · Attribution Agency OS · Dashboards Phoenix · Clinic Revenue HealthPro 360 · PMS/HMS AI Patient Lifecycle Bots AI Lead Management System Smart Appointment System Healthcare CRM Patient Feedback System AI, Analytics & Automation Digital Transformation Calculators Free Digital Health Audit →
All 13 calculators → 🎯 Business Exploration Matrix (New) Dental Clinic Setup IVF Clinic + Lab Setup Multi-Specialty Hospital Setup Aesthetic / Cosmetology Clinic Dermatology Clinic Setup Generic Clinic Setup Physiotherapy Clinic Setup Diagnostic Centre Setup CAC Calculator CPQL Calculator Franchise ROI Calculator Revenue Leakage Calculator CRM ROI Calculator
All Events Workshop 1 · Jun 13 · AI in Clinical Practice Workshop 2 · Jun 27–28 · AI in Growth & Governance Hospital Ops Workshop · Jul 12 Pre-Summit Seminar · Aug 16 Grand Summit 2.0 · Oct 10–11 Bihar AI Summit · Recap AI Innovation Awards · Aug 22 Grand Summit 2.0 · Oct 2026 Aarambh 2026 Recap
Case Studies Insights & Blog Research Reports Calculators AI in Healthcare Digest
Our Story Leaders @ Ichelon · IN · US · AU Ichelon India · Gurgaon Ichelon Global · Dallas, TX Ichelon Australia · Sydney Speakers & Panelists Client Elevation Programme 🤝 Partner Connect 🇦🇪 ICG UAE Careers
Book a Growth Diagnostic
We Do It Right. The right diagnosis. The right strategy. The right systems. Giving healthcare leaders the confidence to make better decisions, build stronger operations, and achieve sustainable growth. — Team Ichelon
Trusted by 150+ healthcare & life-sciences brands
Johnson & Johnson
Mankind Pharma
Adonis Phyto
Narang Biotec
Medanta
Redcliffe Labs
Sitaram Bhartia
Metro Hospitals
Tulasi Hospital
Bloom IVF
Milann
Prime IVF
MedLinks
Handa
Bhardwaj
Eye Q
Johnson & Johnson
Mankind Pharma
Adonis Phyto
Narang Biotec
Medanta
Redcliffe Labs
Sitaram Bhartia
Metro Hospitals
Tulasi Hospital
Bloom IVF
Milann
Prime IVF
MedLinks
Handa
Bhardwaj
Eye Q
Johnson & Johnson
Mankind Pharma
Adonis Phyto
Narang Biotec
Medanta
Redcliffe Labs
Sitaram Bhartia
Metro Hospitals
Tulasi Hospital
Bloom IVF
Milann
Prime IVF
MedLinks
Handa
Bhardwaj
Eye Q
US compliance pillar · HIPAA · 2026

HIPAA-compliant healthcare marketing guide (2026 update)

A practical field guide for marketing leads, growth heads and practice operators inside covered entities and their agencies. Written against the current Office for Civil Rights guidance on online tracking technologies, the Privacy Rule marketing provisions, and the Business Associate rules that decide which vendors you can actually put in front of Protected Health Information.

Backed by App\Support\NamedExperts::get(). --}}
Direct answer
  • HIPAA does not ban marketing. It defines marketing narrowly under 45 CFR 164.501, and requires prior written authorisation for anything that falls inside that definition — with a short list of statutory exceptions.
  • The 2022 and 2024 Office for Civil Rights bulletins on online tracking technologies are the current controlling guidance. IP addresses combined with health-condition URLs or authenticated user identifiers are PHI when disclosed to a third party without a Business Associate Agreement.
  • Meta and Google will not sign a HIPAA BAA for their standard consumer ad platforms. Every server-side CAPI implementation must therefore ship with field-level scrubbing, URL rewriting for condition pages, and consent-mode signals that enforce data minimisation.
  • Common enforcement patterns in recent OCR resolution agreements — including several multi-hospital settlements — involve pixels on patient portals, appointment-scheduling flows, and symptom-checker pages. Fix these three before anything else.
  • The safe-harbour architecture is: consented, de-identified, server-side. Get all three and most tracking use-cases become defensible.
The ICG engagement model
Every practice welcome — engagements from $499/mo.
Goal-linked packages · Fixed retainer + Goal-based Variable Pay · 19-month average client retention — industry-leading. Read the full engagement model →
{-- Agency OS thumbnail · 2026-09-20 --}
Foundation

Who HIPAA actually covers — and where marketing sits

The Health Insurance Portability and Accountability Act of 1996, together with its 2003 Privacy Rule and 2013 Omnibus Rule, applies to two kinds of entity. Covered entities are health plans, health-care clearinghouses, and health-care providers who transmit any health information in electronic form in connection with a HIPAA transaction. Business associates are the vendors, contractors and agencies who create, receive, maintain, or transmit Protected Health Information on behalf of those covered entities.

If a marketing agency, martech vendor, analytics provider, hosting platform or CRM touches PHI in any of those four modes, it is a business associate. Signing a Business Associate Agreement is not a formality — it is what pulls the vendor inside the HIPAA enforcement perimeter and makes them directly liable under 45 CFR 164.502(e) and 164.504(e).

What is Protected Health Information

PHI is individually identifiable health information held or transmitted by a covered entity or business associate, in any form. The 18 identifiers listed under the Safe Harbor de-identification method at 45 CFR 164.514(b)(2) include name, dates more granular than year, geographic subdivisions smaller than a state (with a specific ZIP-code carve-out), telephone and fax numbers, email addresses, Social Security numbers, medical record numbers, health plan beneficiary numbers, biometric identifiers, full-face photographs, IP addresses, and device identifiers.

IP address is the identifier that matters most for marketing. An IP address on its own is arguably not PHI. An IP address paired with a page URL that reveals a health condition, a specialty, a treatment or an appointment intent — as OCR has now clarified twice — is PHI in the hands of a third-party tracker.

The marketing rule

What HIPAA calls "marketing" — 45 CFR 164.501

The Privacy Rule marketing definition is narrower than what a growth team would typically call marketing. It is a communication that encourages the recipient to purchase or use a product or service — with three carve-outs.

  • Face-to-face communication made by a covered entity to an individual.
  • A promotional gift of nominal value provided by the covered entity.
  • A communication for the individual's own treatment, case management or care coordination, or to describe a health-related product or service provided by the covered entity itself — subject to the third-party payment restriction added in the 2013 Omnibus Rule.

Anything else that meets the definition — a paid email campaign, a segmented push notification, a retargeting audience, a co-marketing arrangement with a device manufacturer — requires prior written authorisation from the individual under 45 CFR 164.508(a)(3). The authorisation itself must state that remuneration is involved when applicable, and it must be revocable.

Citation: 45 CFR 164.501; 45 CFR 164.508(a)(3); HHS 2013 Omnibus Rule preamble.

Common misreadings of the rule

The most common misreading in marketing organisations is treating "treatment communications" as a blanket exemption. It is not. The exemption covers communications about the individual's own treatment — an appointment reminder, a follow-up on a prescribed therapy, a preparation instruction for an upcoming procedure. It does not cover a campaign to a broad patient list encouraging them to try a new service line, even if that service line is clinically relevant.

The second common misreading is that de-identified data is free of marketing rules. De-identified data (Safe Harbor or Expert Determination under 45 CFR 164.514) is outside HIPAA — but the process of de-identifying is not. If the source dataset is PHI, an internal analytics workflow that de-identifies before hand-off to a marketing vendor needs to happen entirely inside the BAA-covered perimeter.

Tracking technologies

The OCR tracking-technology guidance — what changed in 2024

In December 2022 the Office for Civil Rights issued a bulletin on the use of online tracking technologies by HIPAA covered entities and business associates. In March 2024 OCR updated that bulletin. Both are the current controlling guidance and both should be read by anyone signing off on a healthcare martech stack.

The 2022 bulletin took a broad view — any combination of an IP address with an authenticated portal page, an appointment page, or a condition page created a disclosure of PHI to the tracking vendor. Providers argued this was over-broad because it swept in visitors who had no relationship with the entity.

The March 2024 update refined the position. OCR now distinguishes between authenticated pages (still clearly PHI when tracked) and unauthenticated pages, where the analysis depends on whether the tracked activity relates to an individual's past, present, or future health, health care, or payment for health care. A visitor reading the "about our hospital" page is not creating PHI. A visitor reading the "cancer screening" page with a tracker that captures IP address plus URL almost certainly is.

Common violation pattern. A regional provider deploys a standard pixel across every page of the website, including the symptom checker, condition landing pages and the appointment-booking flow. Every event is forwarded to a consumer ad platform for retargeting. There is no BAA (the ad platform will not sign one). Every event with a condition-relevant URL is an unauthorised disclosure of PHI. In multiple recent OCR resolution agreements, this exact pattern has resulted in six-figure and seven-figure penalties and multi-year corrective-action plans.
Business Associate Agreements

Which vendors need a BAA — and which won't sign one

A BAA is the contractual instrument required by 45 CFR 164.504(e) whenever a covered entity discloses PHI to a business associate. The BAA must contain specific provisions on permitted uses and disclosures, safeguards, subcontractor flow-down, breach notification, and termination.

Vendors that will sign

  • Enterprise CRM platforms with a healthcare or life-sciences tier.
  • Enterprise email platforms with a HIPAA add-on and audit logging.
  • Cloud infrastructure providers (AWS, Google Cloud, Microsoft Azure) — but only when configured under their HIPAA-eligible services list.
  • Certain analytics vendors that operate a dedicated healthcare product line.
  • Marketing agencies with a documented HIPAA program — an executed BAA, an annual risk assessment, and workforce training records.

Vendors that will not sign for their standard ad products

  • Consumer ad platforms (Google Ads, Meta Ads, LinkedIn Ads, TikTok Ads for Business, X Ads).
  • Consumer analytics products.
  • Most consumer-grade tag managers when deployed without an intermediary server.

Where a vendor will not sign a BAA, the architectural answer is not "trust them anyway." It is to insert a HIPAA-safe intermediary — usually a server-side event pipeline — that receives events inside the BAA-covered perimeter, strips or hashes any identifier that would make the event PHI, and forwards only what is safe to send.

Server-side architecture

CAPI, server-side tagging and the safe-harbour pattern

A defensible healthcare tracking architecture in 2026 has five components.

  • A consent management platform that respects an authorised user's revocation and a website visitor's opt-out. Consent Mode signals must flow into every downstream vendor.
  • A server-side tagging container hosted on a first-party domain, deployed inside the covered entity's or business associate's infrastructure.
  • Field-level allow-listing. Only fields on a positive allow-list are ever forwarded. Everything else — including URL query strings, referrer chains, and any identifiers not explicitly listed — is dropped at the edge.
  • URL rewriting for condition-specific pages before any event leaves the server. A visit to /cancer-screening becomes an anonymised event token before it is forwarded to a non-BAA vendor.
  • Audit logging retained for the HIPAA six-year period so that a Compliance Officer can reconstruct what left the perimeter and when.
Safe-harbour pattern. Authenticated portal pages have zero third-party tags. Unauthenticated condition pages route through server-side tagging with field-level scrubbing. Conversion events forwarded to ad platforms carry only a hashed anonymous ID, an event name and an event value. All PHI-adjacent fields (IP address, page URL, referrer) are dropped at the server edge. Consent state is honoured in the same request.
Fix the top-3 first

The three highest-risk surfaces on a healthcare website

1. Patient portal

Any tag on an authenticated portal page is PHI-adjacent by default because the user is logged in. Strip everything except first-party analytics inside the BAA perimeter.

2. Appointment scheduling

Provider, specialty and time selection combined with an IP address is a PHI disclosure when forwarded to a non-BAA vendor. Server-side event forwarding with URL rewriting is the fix.

3. Symptom checker and condition pages

These are the highest-intent SEO surfaces and the highest-risk tracking surfaces. Route them through the server-side pipeline before any ad or analytics vendor receives an event.

Marketing authorisation

When you actually need a signed authorisation — and what it must say

A HIPAA marketing authorisation under 45 CFR 164.508 is a specific instrument, not a checkbox. It must describe the information to be used or disclosed, name the covered entity and the recipient, describe each purpose, carry an expiration date or event, be signed and dated by the individual, contain a statement of the right to revoke, contain a statement that the covered entity may not condition treatment or payment on the authorisation, and contain a statement that PHI once disclosed may be re-disclosed by the recipient and no longer protected. If remuneration is involved, that fact must be disclosed on the authorisation form itself.

In practice most healthcare marketing does not require a marketing authorisation because it either qualifies for the treatment carve-out, is directed at leads who are not yet patients, or uses de-identified data. The two moments that most often demand a fresh authorisation are: co-marketing arrangements with device or pharma partners, and third-party lists purchased or exchanged with other covered entities.

HIPAA TCPA ADA CAN-SPAM FTC State medical boards
Enforcement patterns

What OCR has actually enforced — patterns from recent resolution agreements

Pattern-matching against the OCR resolution agreements catalogue is the fastest way to calibrate a risk register. Themes that recur across recent settlements include tracking pixels on patient-portal login flows, tracking pixels on symptom checkers, unencrypted email exchanges of PHI with marketing vendors, and email campaigns to former patients without a valid authorisation on file.

The 2024 tracking-technology bulletin update should be read alongside the earlier Anthem, Premera, Fresenius and Lifespan settlements. The common thread is not the specific technology — it is the failure to run a HIPAA risk analysis before deploying it. A risk analysis under 45 CFR 164.308(a)(1)(ii)(A) is a required administrative safeguard, and its absence is what turns an incident into a wilful-neglect finding.

The penalty tiers

HITECH civil monetary penalties are structured in four tiers based on culpability, with per-violation floors and ceilings and an annual cap per identical provision. The 2024-adjusted range is approximately USD 141 per violation at the "did not know" tier up to USD 71,162 at the "wilful neglect, not corrected" tier, capped at approximately USD 2.13 million per identical provision per calendar year. State attorneys general can bring parallel actions under HITECH section 13410(e). Criminal penalties under 42 USC 1320d-6 apply where PHI is knowingly obtained or disclosed for personal gain.

Trifecta · adapted for HIPAA

Angryturtle · SIE · YODA — the HIPAA-safe version

Angryturtle · GBP OS

Google Business Profile posts, review responses and Q&A moderated for PHI. Never confirm a specific patient's presence in a review response; use the sanctioned de-identified reply pattern.

SIE · Search Intelligence Engine

Condition, treatment and specialty topic maps written for AI Overview and traditional SERP intent — with all tracking on those pages routed through the server-side pipeline.

YODA · YouTube AIO

Physician-led educational content produced without PHI, with review by the practice's Compliance Officer before publish. Comment moderation policy screens for accidental PHI disclosures by commenters.

Leadership

Backed by ICG global leadership

Every HIPAA-scoped engagement has direct line-of-sight to the Ichelon Global Leadership Team and a senior reviewer who has scaled US healthcare accounts through the 2022 and 2024 OCR tracking-technology transitions.

The ICG technology stack

Nine tools. One compounding system. HealthApex OS
Built in-house. Deployed in every engagement.

ICG's results are reproducible because they are built on proprietary infrastructure — not agency intuition or generic tools. These nine HealthApex OS platforms are what power every ICG engagement.

Healthcare CRM

Nexus CRM

Healthcare CRM & Lead Management

ICG's healthcare-specific CRM and lead management system. Specialty-configured funnel stages for IVF, dental, aesthetic, ortho, hospital OPD. 1-click CAPI + GCLID via Beacon. Hawk intelligence built in. DPDP-compliant by architecture. Deployed across 300+ healthcare centres.

  • Specialty-specific funnel stages, not generic SaaS pipeline
  • 1-click CAPI + GCLID via Beacon attribution
  • Telecaller leaderboard + adherence scoring native
  • DPDP Act 2023 compliant by architecture
Explore Nexus CRM →
Business Layer

Hawk

CRM Intelligence & Lead-Ops MIS

Sits as the business intelligence layer above your CRM — Nexus, Salesforce, LeadSquared, HubSpot, Zoho, or any custom CRM. Shows where leads are leaking, which effort is wasted, and which good leads were quietly downgraded by automation — not by a human decision.

  • Sits above your existing LMS — no replacement
  • 83% of effort goes to dead leads — surfaced Day 1
  • ~75% qualified-lead downgrades by automation
  • Free Lead-Leak Audit in 48 hours
Explore Hawk + free audit →
Attribution Core

Beacon

Attribution Engine & CAPI Middleware

Sits at the centre of every ICG attribution architecture. CAPI middleware connecting Meta Ads, Google Ads, WhatsApp and IVR to your CRM. Lifts Event Match Quality from 2.5 to 6+, reducing CPM 30–40% from the same budget.

  • Server-side CAPI — bypasses iOS privacy changes
  • EMQ 2.5 → 6+ across portfolio
  • 30–40% CPM reduction from EMQ lift alone
  • Multi-touch: ad → consultation → revenue
Explore Beacon →
Practice Management

HealthPro 360

PMS with built-in revenue intelligence layer

The only PMS that tracks cross-sell and up-sell opportunities within your existing patient base. 12 modules covering OPD, IPD, Pharmacy, Labs, Billing, Inventory, Patient Portal, Smart Scheduling, RBAC, AES-256 encrypted storage.

  • Only PMS with built-in Revenue Intelligence
  • Cross-sell signal tracking within existing patients
  • 12 modules: OPD, IPD, Pharmacy, Labs, Billing+
  • Audit trails + RBAC + AES-256 encryption
Explore HealthPro 360 →
Revenue Layer

Phoenix

Revenue intelligence built over your existing PMS

If you already have a PMS — Akhil Systems, Practo, or any other — Phoenix builds the business intelligence layer on top of it without replacement. Currently live across 46 centres for a national chain.

  • Works over your existing PMS — no migration
  • Daily action queue: Prevent Loss / Maintain / Grow
  • Catches unbilled services, collection gaps, lapsing patients
  • CPQL variance ₹620–₹3,800 → ₹680–₹1,420
Explore Phoenix →
YouTube Intelligence

YODA

YouTube analytics that measures patients, not views

The only YouTube intelligence platform built for healthcare business outcomes. Connects video performance to actual consultation bookings — not views, not subscribers. Patient testimonial videos generate 6.9× more consultations per view than condition explainers.

  • Consultation attribution per video — not views
  • Demand-gap: what patients search that your channel misses
  • 50+ doctor channels tracked across India
  • AIO readiness scoring: which videos AI tools cite
Explore YODA →
Governance & Transparency

Agency OS

Full transparency. Instant diagnosis. Zero surprises.

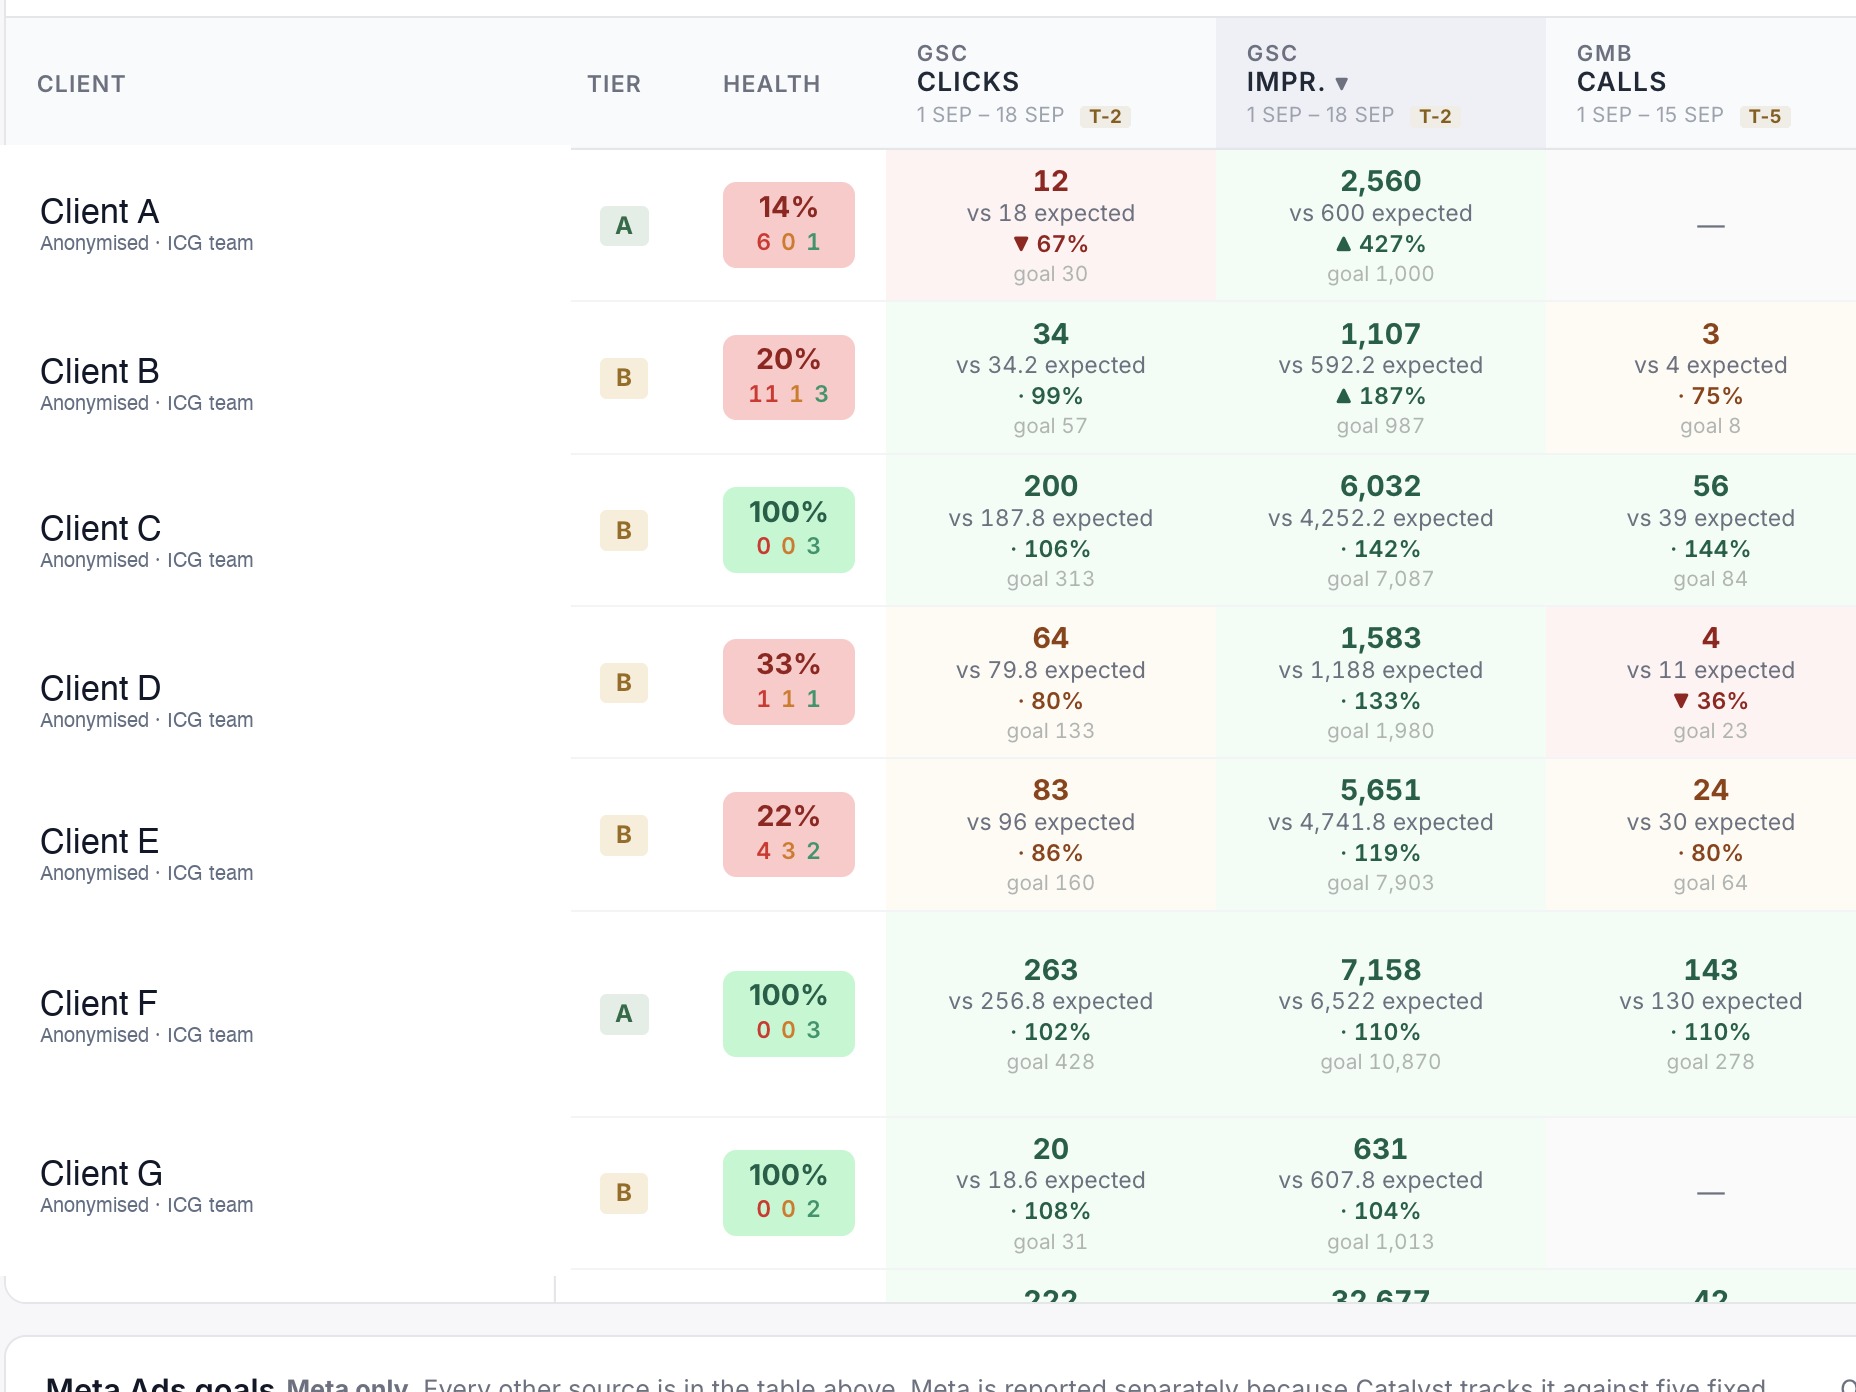
ICG's centralised governance platform — every client sees everything in real time, and ICG's team sees every problem the moment it surfaces. 30+ real-time alert systems fire the moment a metric drifts outside its performance envelope.

  • GSC, GA4, Google Ads, Meta Ads, IVR — one live view
  • 30+ real-time alert systems per account
  • CPQL drift alert at >15% week-on-week change
  • Client login: full transparency on your account
Explore Agency OS →
AEO & LLM Intelligence

AIO Intel

AI Overview + LLM citation tracking, healthcare-tuned

Knows the moment ChatGPT, Perplexity, Google AI Overviews and Gemini cite your brand in patient answers — and which content drove the citation. Bot-aware dashboard with GA4-registered custom dims (AIO source, AIO referrer) and IndexNow + GSC API integration.

  • Live tracking across ChatGPT / Perplexity / Google AIO / Gemini
  • Bot-aware: knows human vs scraper traffic
  • Custom GA4 dims register AIO source + referrer
  • IndexNow + GSC API: content surfaced to LLMs within hours
View AIO Intel dashboard →
Competitor Intelligence

Prism Spy

Every Meta + Google ad your competitors run, watched daily

Tracks 75+ Indian healthcare brands, 2,150+ active ads, ₹50Cr+ aggregate ad spend visibility per month. Surfaces what's working, what's been killed, what offers are emerging. Powers every ICG Meta Ads brief, Performance Marketing diagnostic, and IVF / derm / dental specialty campaign with real competitive intelligence.

  • 75+ brands tracked across 30+ healthcare specialties
  • 2,150+ active ads · daily refresh
  • Activity Feed: every spend / hook / pause logged
  • Offers Intelligence: 250+ offers in market tracked
Explore Prism Spy →
GBP Intelligence Platform

Angryturtle

Every Google Business Profile scored, tracked, protected, and grown from one command centre

ICG's proprietary Google Business Profile intelligence platform. Scores every listing across 7 dimensions, tracks rank on a live geo-grid across your actual service area, audits NAP + citations, monitors 531 suspension-risk factors continuously, and drafts Google Posts on cadence. Currently managing 143 healthcare listings with 0 suspensions and 4.76★ portfolio average across 28,137 reviews.

  • 143 listings under management · 0 suspensions · 4.76★
  • 7-dimension Health Score + 5-factor Rank OS per listing
  • Geo-grid rank tracking + NAP + Citation audit + Profile Shield
  • NMC + NABH + ART Act + DPDP compliance built into every content + review workflow
Explore Angryturtle →

Every ICG engagement runs on some combination of these ten HealthApex OS tools. The diagnostic determines which combination is right for your practice.

Explore HealthApex OS → See the full stack live on your account — free 30-min audit
The team behind your account

Every diagnostic is led by a founder.
You'll know their names before the engagement begins.

ICG was built by three IIT BHU engineers who entered healthcare marketing with a specific intent: to build the tools that didn't exist and run the campaigns that most agencies couldn't. When you book a diagnostic, Rohit or Abhash leads it personally. Not an account manager. Not a senior executive. The people who built what you're evaluating.

The ICG team — 60+ healthcare marketing specialists at Gurgaon HQ

60+ specialists.
One growth engine.

Performance marketers, analysts, AI engineers, content strategists, and operations specialists — all healthcare-only. Headquartered in Gurgaon since 2018.

Rohit Gupta — Leader, ICG

Rohit Gupta

Business & Growth Lead & Director

IIT BHU · IIM Rohtak

Rohit's first question in every diagnostic: "When you ask your agency why patients aren't booking — what do they say?" He says the answer tells him more than any dashboard.

Full profile →
Abhash Kumar — Leader, ICG

Abhash Kumar

Strategy & Analytics Lead & Director

IIT BHU · IIM Bangalore

Abhash built Beacon because most agencies couldn't answer one question: "Which of my campaigns generated that consultation?" He decided the problem was solvable in code. It was.

Full profile →
Deep Das — Leader, ICG

Deep Das

Technology & AI Lead & Director

IIT BHU

Deep built the 4-Bot patient lifecycle system after watching a client lose 60+ qualified leads in one week to a 6-hour WhatsApp response window. He decided the problem was solvable in code. It was.

Full profile →
FAQ

HIPAA marketing — common questions

Is a website visitor considered a patient under HIPAA?

An anonymous website visitor is not automatically a patient. Per the March 2024 OCR bulletin update, a visitor becomes a subject of PHI only when tracked activity relates to an identifiable individual and to past, present, or future health care.

Do we need a Business Associate Agreement with Google or Meta?

Neither Google nor Meta will sign a HIPAA Business Associate Agreement for their consumer ad platforms. That is why PHI must be scrubbed before any event reaches them, and why server-side conversion APIs with field-level control are the standard architecture.

What counts as marketing under the HIPAA Privacy Rule?

Under 45 CFR 164.501, marketing is a communication that encourages the recipient to purchase or use a product or service. Face-to-face communications, promotional gifts of nominal value, and treatment communications are excluded.

Can we retarget patients who visited a specific condition page?

Condition-based retargeting is the exact scenario OCR called out. Combining a condition URL with a visitor identifier creates PHI, and forwarding that to an ad platform without authorisation and a BAA is a disclosure violation.

What are the penalties for a HIPAA marketing violation?

Civil penalties under HITECH tiers range from about USD 141 to USD 71,162 per violation, capped at approximately USD 2.13 million per identical provision per year (2024-adjusted). Wilful neglect not corrected sits at the top tier.

How do we run analytics on a HIPAA-scoped site?

Use an analytics provider that will sign a BAA, or route data through a HIPAA-safe warehouse first, scrub identifiers and health-related URLs, and forward the sanitised dataset to a non-BAA analytics for aggregate reporting only.

Scope your HIPAA-safe marketing engagement

Book a 30-minute call with a member of the Leadership Team, email the US practice lead, or WhatsApp us in your time zone. Retainers are custom-scoped per engagement · from Rs 20,000/month equivalent (approx USD 250 / AUD 370).

Selected ICG clients

Healthcare brands ICG
has worked with.

A representative slice of the 300+ healthcare brands ICG has delivered for across India. Full client list available under NDA during a Brand and Growth Diagnostic.

Read full client case studies →

Chat with the Leadership Team
🎯 Goal-linked · Fixed + Goal-based Variable Pay · 19-mo retention
Chat with the Leadership Team