What does the FTC Health Breach Notification Rule mean for health app marketing?
The FTC Health Breach Notification Rule means most consumer health apps must treat ad pixels, SDKs and audience uploads as possible breaches. Since July 2024, the rule covers apps that hold health data outside HIPAA, and an unauthorized disclosure to an advertising platform counts as a breach. That triggers notice to users, the FTC and sometimes the media, so marketing setups need user authorization and a careful data audit.
- Most consumer health apps are covered if they are outside HIPAA and can draw data from more than one source.
- An unauthorized disclosure is a breach. Health data sent to ad or analytics platforms without user authorization can trigger the rule.
- Notice runs on a 60-day clock to users, plus the FTC and media when 500 or more people are affected.
- Growth still works with neutral events, no ad tags on health screens, and contracts that limit vendors.
- Every practice welcome — retainers from $499/mo, Goals-Driven engagements, Performance-Linked Payout Models available.
- Dallas, Texas LLC
- US client team · Central Time (CST)
- 25+ US healthcare clients
- BAA signed with every client
- HIPAA compliance training across client and delivery teams
- Contracts and invoices in USD
-
 Primary Care · North Dallas, TXCase study →
-
 MedSpa · North Dallas, TX
-
 Skin Care · Beverly Hills, CA
-
 Dental · Christiansburg, VACase study →
-
 Pediatrics · Blacksburg, VACase study →
-
 Pediatric Dentistry · Blacksburg, VACase study →
-
 Dental · Roanoke, VACase study →
-
 Functional Medicine · Telehealth · USACase study →
“They were able to get all my ideas and work with me over a period of three to four months and create this amazing website. It's super customized, very modern, and it incorporates all the elements that I had wanted — the patient portal, nice pictures, a very interactive website, patient reviews. I would highly recommend their company to anyone who wants to make an excellent website.”
Does the Health Breach Notification Rule apply to my health app?
It probably does if your app or site holds identifiable health information for consumers, can pull that data from more than one source, and you are not a HIPAA covered entity or business associate. The rule was written for personal health records. The 2024 amendments made clear that most consumer health apps fit that definition.
The rule lives at 16 CFR Part 318. The FTC finalized its amendments in April 2024, and they took effect on July 29, 2024 (FTC announcement). In September 2026 the FTC withdrew its 2021 policy statement on health apps, saying the updated rule now covers apps and connected devices directly (FTC release). So the question is settled. If you market a direct-to-consumer health app, you should assume the rule is in play until counsel tells you otherwise.
The four tests that decide coverage
| Test | What the rule says | What it means for an app |
|---|---|---|
| Health information | Information about past, present or future physical or mental health, care or payment for care, that identifies a person or reasonably could | Cycle logs, sleep scores, symptom notes, medication lists, weight entries and diet logs all count |
| Created or received by a covered health care provider | The amended definition includes "any other entity furnishing health care services or supplies" | An app that tracks fitness, fertility, sleep, mental health, diet or vital signs is itself treated as furnishing health care services |
| Multiple sources | The record "has the technical capacity to draw information from multiple sources" | User entries plus a wearable sync, a phone health API or a lab upload. The capacity is what matters, even if a user never connects a second source |
| Not HIPAA | HIPAA covered entities and business associates acting as such are excluded | A telehealth practice working under HIPAA is usually outside this rule; its direct-to-consumer wellness app may not be |
The rule names three roles. A vendor of personal health records offers or maintains the record. A PHR related entity offers products through the vendor's app or site, or sends data into it. A third party service provider handles the data for either of them. Marketing teams usually sit at the vendor. Their analytics and ad partners can sit in the other two roles.
The FTC publishes a mobile health app interactive tool, which also covers HIPAA and FDA rules, that walks a developer through which federal laws may apply. It is worth ten minutes before a launch.
Why can sharing data with an ad platform count as a breach?
Because the amended rule says a breach includes "an unauthorized disclosure", not just a hack. If your app sends identifiable health information to an advertising or analytics company without the user's authorization, the FTC can treat that as a breach of security. That triggers notice duties and, if you stay quiet, penalties.
This is the part most growth teams miss. The definition in section 318.2 now ends with one plain sentence: a breach of security "includes an unauthorized acquisition of unsecured PHR identifiable health information in a personal health record that occurs as a result of a data breach or an unauthorized disclosure." Nobody has to break in. A tag that fires on the wrong screen can do it.
The FTC's first two cases under the rule, both in 2023, were about exactly this. One involved a prescription discount and telehealth company. The other involved an ovulation-tracking app. In both, the FTC said the companies shared health data with advertising platforms in ways that contradicted their privacy promises, and did not report it (FTC summary). The settlement orders barred both companies from sharing health data for advertising.
Three patterns that create the problem
- Event names that describe health. An event called "pregnancy_week_12" or "started_anxiety_program" tells the receiving platform something about a person's health, tied to a device ID or hashed email.
- Customer list uploads. Uploading app users to build lookalike or retargeting audiences discloses that each person uses a health app, and often which one.
- SDKs you did not configure. Software development kits for attribution, crash reporting or ads can collect more than you expect. They often collect it by default.
None of this means a health app cannot advertise. It means the data that leaves your app needs a deliberate decision behind it, and the user's authorization where health information is involved.
Which marketing tools create exposure under the rule?
Any tool that receives data from inside your app or logged-in site can create exposure. The usual suspects are ad pixels, mobile SDKs, server-side conversion feeds, customer-list audiences, email and SMS platforms, and session-replay tools. Map each one, list what it receives, and decide whether health information is in that stream.
| Tool | Typical exposure | Lower-risk setup |
|---|---|---|
| Ad pixel or ads SDK in the app | Screen views and events tied to device IDs; event names can reveal conditions | Remove from logged-in and in-app health screens; send only non-health events such as "account_created" with user authorization |
| Server-side conversion feed | Same data as a pixel, sent from your server, so it is easy to forget | Treat it like a pixel; strip health fields and condition-specific product names |
| Customer-list audiences | Reveals that each person is a user of a health product | Use only with clear authorization, or replace with contextual and interest-free targeting |
| Product analytics | Detailed behavior inside health features | Use a vendor contract that bars the vendor from using the data for its own purposes; minimize fields |
| Session replay | Can capture typed symptoms, notes and form fields | Mask all inputs by default or keep it off health screens |
| Email and SMS platforms | Lists, segments and message content that imply health status | Neutral subject lines; segment names that do not describe conditions; documented consent |
Run this audit with your engineer, not from the marketing dashboard. Dashboards show what a tool reports. Network logs show what it actually receives. Repeat the audit after every major release, because a new feature can add a new event without anyone in marketing knowing.
For practices and telehealth groups that are covered by HIPAA, the tracking problem looks different but rhymes. Our guide to HIPAA-safe website tracking covers that side.
What does user authorization look like in practice?
The rule turns on whether a disclosure was authorized by the individual. The FTC's cases treated sharing that went beyond what the company told users as unauthorized. So authorization should be clear, specific to the sharing, and given before the data moves. Counsel should sign off on the wording and the flow.
A safe working model has four parts.
- Say it plainly, in the flow. A screen that says what goes to whom and why, at the moment it matters. A link to a long privacy policy is a weak substitute.
- Make it a real choice. The app should work if the user says no. Pre-checked boxes and "accept all" walls do not read as a free choice.
- Match the promise to the code. If the privacy policy says you never share health data for advertising, no SDK should be able to do it. This mismatch sat at the center of the 2023 cases.
- Keep records. Log what each user agreed to, when, and on which version of the screen.
Some state laws ask for more than this. Washington's consumer health data law requires separate consent for collection and for sharing. Our guide to state consumer health data laws explains how those rules stack on top of the FTC rule.
Wording to avoid in your own marketing
Do not write "HIPAA-compliant" on an app that HIPAA does not cover. It suggests a legal protection the user does not have. Describe what you actually do: what you collect, what you share, and with whom.
What must a health app do after a breach?
Notify affected users without unreasonable delay and no later than 60 calendar days after discovery. Notify the FTC at the same time if 500 or more people are affected. Notify prominent media if 500 or more residents of one state are affected. The notice has required contents, including who received the data.
| Who must be told | Deadline | Notes |
|---|---|---|
| Affected individuals | Without unreasonable delay, no later than 60 calendar days after discovery | Email is allowed if the user chose email as the primary contact method; the rule pairs it with a text, in-app message or banner |
| FTC, 500 or more people | At the same time as the individual notices | Uses the FTC's notification form |
| FTC, fewer than 500 people | Logged and reported within 60 days after the end of the calendar year | Keep the log current |
| Media | Within 60 calendar days, when 500 or more residents of a state, DC or a territory are affected | Supplements individual notice, does not replace it |
| Third party service provider to its client | Without unreasonable delay, within 60 days | Must get acknowledgment that the notice was received |
These deadlines come from section 318.4. The notice itself must describe what happened, the dates, the types of health information involved, the identity of third parties that acquired the data, the steps users can take, what you are doing about it, and at least two ways to contact you (FTC compliance guide). It must be clear and conspicuous, in plain words.
The burden of proof sits with the company. You must be able to show that every notice went out as required. Violations are treated as unfair or deceptive practices, with civil penalties per violation that the FTC adjusts each year for inflation.
What marketing owns in a breach
Legal owns the decision. Marketing usually owns the words and the channels: the email, the in-app message, the help-center page, the press statement and the social replies. Draft templates in advance, get counsel to approve them, and decide who can send them. A breach week is the wrong time to write from scratch.
How should a health app grow without risking a rule violation?
Build acquisition around channels that do not need health data to leave your app. Search ads on non-health keywords and landing pages, content and SEO, app store optimization, partnerships, and contextual placements can all drive installs. Measure them with aggregated, consented data instead of user-level health events.
- Split the funnel at sign-up. Pages before an account exists can usually carry standard measurement, provided they do not ask health questions. Screens after sign-up should carry no ad tags by default.
- Measure the top, model the rest. Count installs and account creations by campaign. Use cohort and incrementality reads for downstream value rather than sending health events back to ad platforms.
- Write neutral events. If you send any conversion, call it "trial_started", never something that names a condition or program.
- Treat lists as sensitive. Do not upload user lists to ad platforms unless users authorized that use.
- Put it in contracts. Agency and vendor agreements should bar any use of your users' data beyond your instructions.
- Review claims too. The FTC's health claims standard applies to app benefit claims. "Improves sleep" needs evidence just as a supplement claim does.
Our guide to the App Store and Google Play for health apps covers listing copy and privacy labels, which should match what this audit finds.
Who should own this inside a health app company?
One senior person should own the line between growth and privacy. In early companies that is often a fractional CMO working with outside counsel and the lead engineer. The job is to keep the ad stack, the privacy policy and the product in agreement, and to sign off on every new tool.
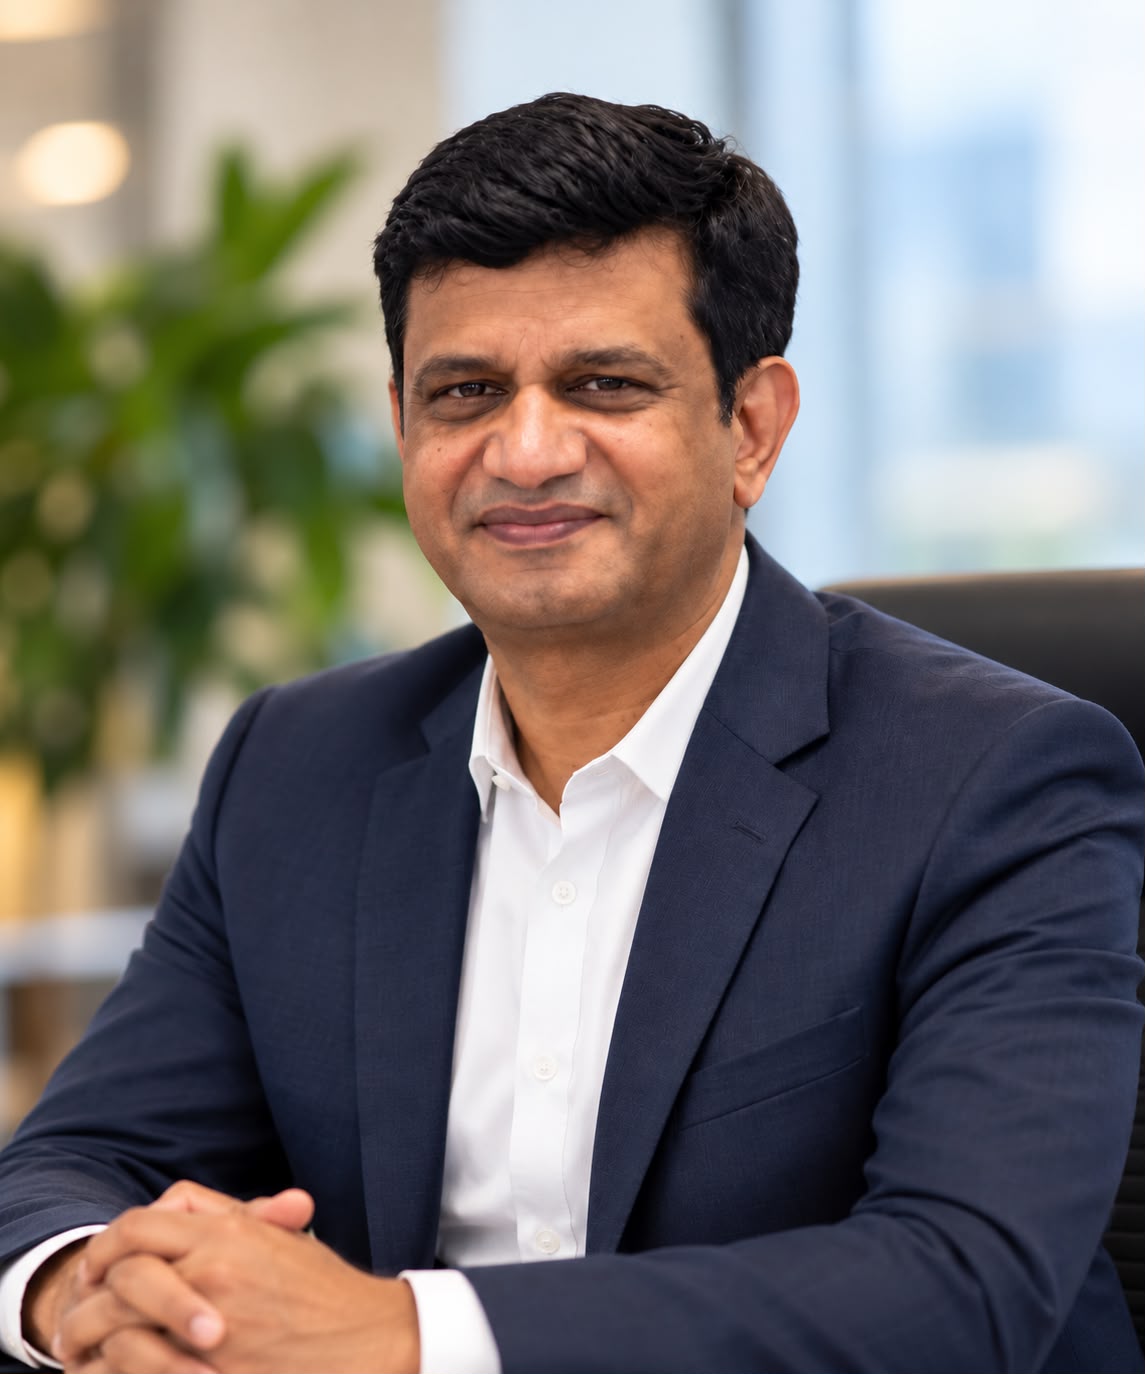
At Ichelon Consulting US, Santosh Reddy, Partner, serves as fractional CMO for healthcare companies, including digital health and app businesses. Plans run from $1,000 to $2,000 a month depending on how embedded the role is. Execution such as ads, SEO and content is scoped separately, and we sign a Business Associate Agreement with every US client. We do not give legal advice. We build marketing that your counsel can approve. See the fractional CMO service, or book a call with the US team and bring your tag list.
Related pages from the US team
Fractional CMO for healthcare companies
Senior marketing leadership that keeps growth and privacy in agreement.
HIPAA-safe website tracking
How covered practices and telehealth groups handle pixels and analytics.
State consumer health data laws
Washington, Nevada and Connecticut rules that stack on the FTC rule.
Digital health startup marketing
Channels and sequencing for a direct-to-consumer health product.
Every practice welcome — Goals-Driven engagements from $499/mo
We benchmark your last 90 days, agree monthly goals with you, and track them live on Ichelon Agency OS with a report every Monday. Performance-Linked Payout Models are available. Our US leadership is based in Dallas, and strategy calls run in US business hours.
Common questions
Does the FTC Health Breach Notification Rule apply to apps covered by HIPAA?
No. The rule excludes HIPAA covered entities and businesses acting as their business associates. A health app run by a practice under HIPAA falls under HIPAA instead. Many consumer apps have no HIPAA relationship at all, and the FTC rule was amended in 2024 to make clear that those apps are covered.
Is sharing app data with an advertising platform a breach under the FTC rule?
It can be. Since the 2024 amendments, a breach of security includes an unauthorized disclosure of identifiable health information, not only a hack. If a health app sends such data to an advertising or analytics company without the user's authorization, the FTC can treat it as a breach that requires notice.
When did the amended Health Breach Notification Rule take effect?
The amendments took effect on July 29, 2024. The FTC finalized them in April 2024. They clarified that health apps and similar technologies are covered, expanded the definition of a breach to include unauthorized disclosures, allowed email-based notice, and added required notice contents such as the identity of third parties that received the data.
How quickly must a health app notify users after a breach?
Without unreasonable delay and no later than 60 calendar days after the breach is discovered. If 500 or more people are affected, the FTC must be notified at the same time. If 500 or more residents of a single state are affected, prominent media serving that area must also be notified.
What should a health app marketing team audit first?
Start with every tool that receives data from logged-in or in-app screens: ad pixels, mobile SDKs, server-side conversion feeds, customer-list audiences, analytics and session replay. Check network traffic, not dashboards, to see what each one actually receives. Remove or neutralize anything that carries health information without user authorization.
Can a health app still run paid ads under the FTC rule?
Yes. The rule limits unauthorized disclosure of health information, not advertising itself. Apps can run search, social and app store campaigns that measure installs and sign-ups with neutral, consented events. The risk comes from sending health events or user lists back to ad platforms without clear user authorization.
A note on this guide: it explains marketing practice, not legal advice. Rules on privacy, advertising and insurance change and vary by state, so confirm anything compliance-related with your own counsel.
Want a second pair of eyes on your app's ad stack?
A 30-minute call with the US team. Bring your list of SDKs and tags. We will show you where health data may be leaving the app and how to keep growing without it.